
Agent Guard
Real-time secret-leak guardrails for AI coding agents (Claude Code, Codex), Git hooks, and CI.
Install
git clone https://github.com/JeongJaeSoon/agent-guardInstall command taken from the project's README or registry entry. Always review code before running it.
README excerpt
Read full README on GitHub →Agent Guard
A local-first guardrail that keeps AI coding agents from leaking your secrets.
Blocks risky
.envreads, masks secret-like output, and scans changes before they reach Git. No hosted account, no telemetry.
Agent Guard is a local-first guardrail for Claude Code, Codex, Git hooks,
GitHub Actions, and direct shell use. It blocks common secret-exposure paths
before a supported tool runs, redacts supported tool output, and scans changed
files after mutations. It uses gitleaks and portable shell; it has no hosted
account, telemetry collector, or developer service.
It is a defense-in-depth boundary. Keep GitHub Secret Scanning, Push Protection, review, and normal credential management in place. Agent Guard is not a vault, DLP system, EDR, or credential rotator.
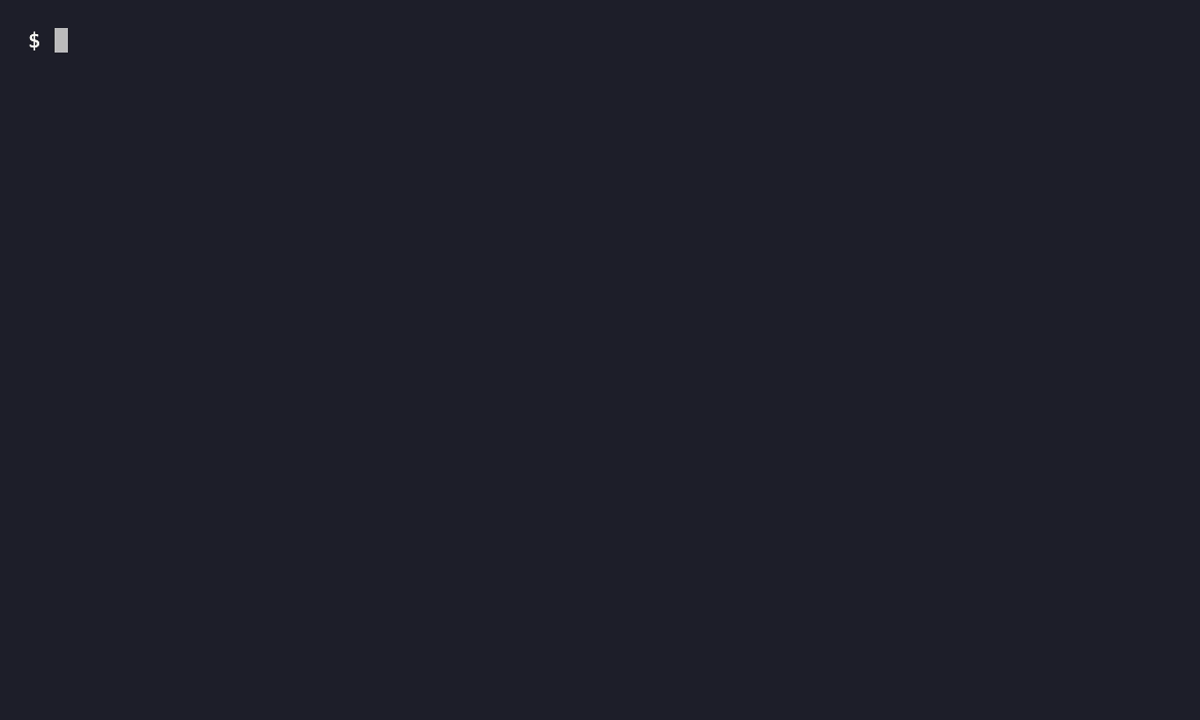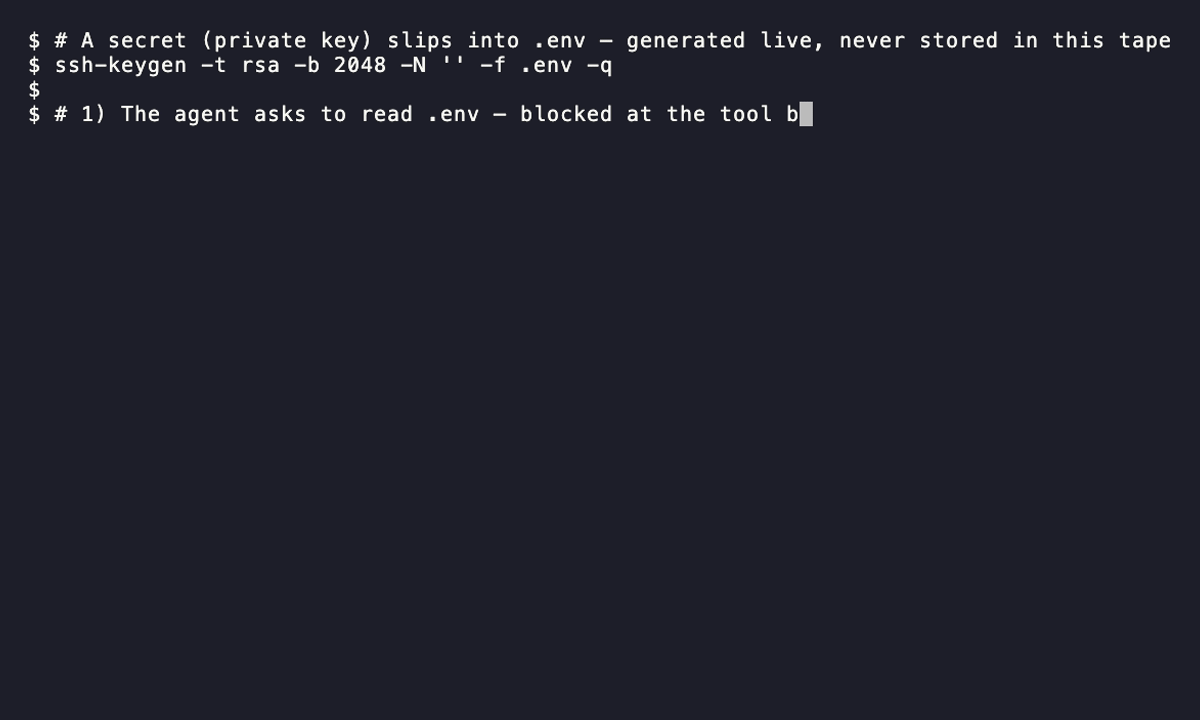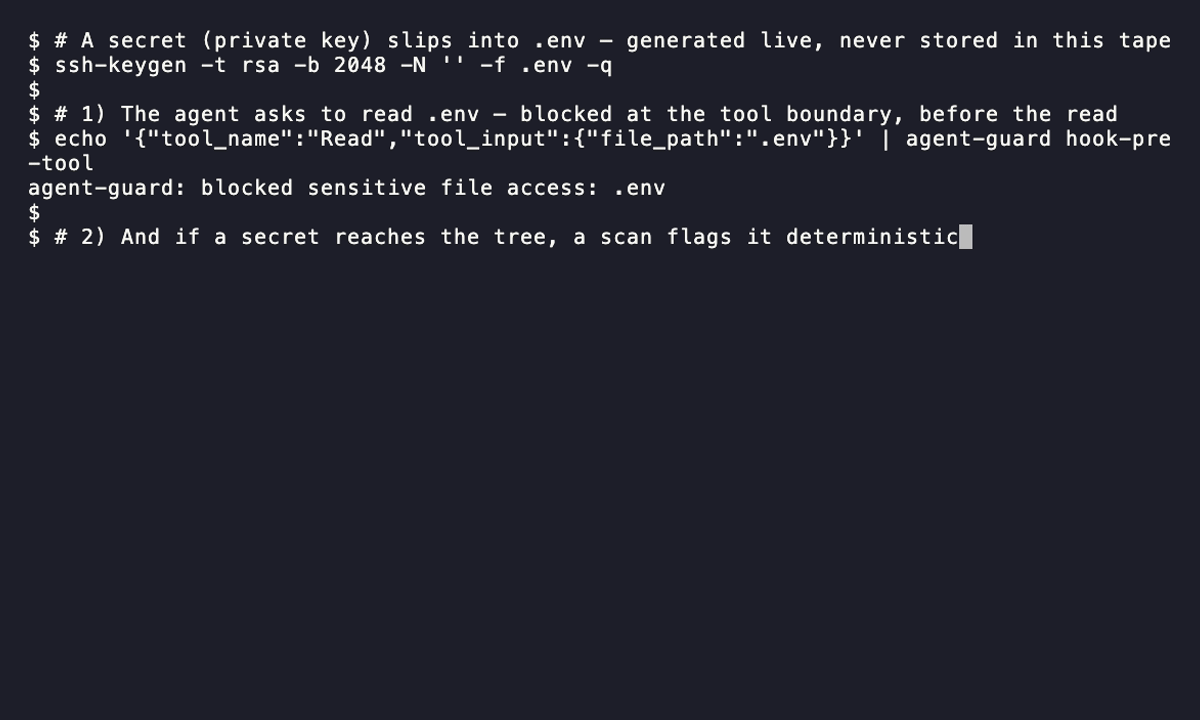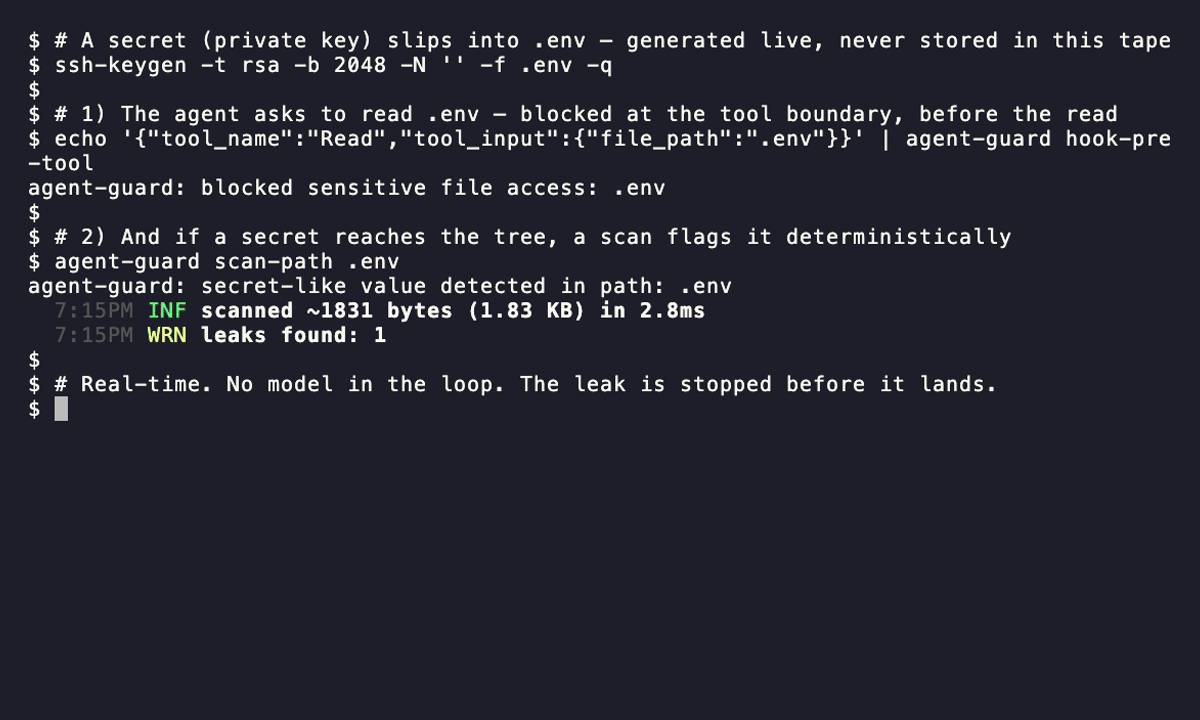
Keep secrets out of Git
A key that lands in a commit lives in history long after you delete the file.
Agent Guard puts a gitleaks scan in front of the commit routes it hooks, so a
detected API key, token, or .env value is stopped before it enters history,
with CI behind it as a backstop:
| Who commits | What stops the leak |
|---|---|
| An agent in Claude Code or Codex | Before the agent's git commit or git push runs, the plugin scans the staged added lines and blocks the command on a secret-like value. It also refuses --no-verify and --no-gpg-sign on those commands, so the agent cannot switch the check off with a flag. |
| Any local commit, yours or an agent's | Once installed, the native pre-commit hook scans the staged added lines after Git has staged everything the commit will include, and aborts the commit on a finding or when the scan cannot run. Git skips it for git commit --no-verify; the plugin refuses that flag for agents, and CI covers the rest. |
| Anyone, after a push | The GitHub Action scans the checked-out files of each push or pull request it runs on, as the repository backstop. |
The plugin scans what the commit would contain. That covers the index and also
the tracked changes Git stages by itself for git commit -a, --patch, or a
pathspec such as git commit , --include, or --only, and the
untracked files that --interactive can add. When an argument is only known at
run time, such as git commit $FLAGS, or the same command runs git add first,
the plugin scans every tracked change and untracked file, including ignored
files after git add -f. Shell code the command line passes to bash -c,
sh -c, a here-string, env -S, or eval is checked like the command
itself, and so is the git command a git alias expands to, read from the
configuration that command would read. When that code, the git subcommand, the
alias, or the working directory is only known at run time, the plugin cannot
tell what the command commits, and the infrastructure policy below decides.
That includes a ! shell alias, a guess help.autoCorrect may run, and an
alias that an earlier part of the same command line may have changed.
Similar plugs


CLI proxy that reduces LLM token consumption by 60-90% on common dev commands. Single Rust binary, zero dependencies

Bash is all you need - A nano claude code–like 「agent harness」, built from 0 to 1

Documented system prompts from Anthropic - Claude Fable 5.1, Opus 5.5, Claude Design, Claude Code. OpenAI - ChatGPT GPT-6-Astra, Codex. Google - Gemini 3.8 Flash, 3.1 Pro,…

Wrap Antigravity, ChatGPT Codex, Claude Code, Grok Build, Muse Code, Devin as an OpenAI/Gemini/Claude/Codex compatible API service, allowing you to enjoy the free Gemini…